
AEU
News and analysis from our engineers.
Docker Hub flaw let tokens act as other users
Docker fixed a critical Docker Hub flaw that could let registry tokens push, pull or delete images as another user.
Ivanti Connect Secure zero-day chain gives root access
Ivanti Connect Secure zero-days were exploited to run root commands, with fixes for two flaws and a third patch still pending.
npm trusted publishing now expires unvalidated setups
npm trusted publishing changes limit a loophole that could let attackers publish new versions of packages they did not own.
LG Smart TV vulnerability enables local root takeover
LG Smart TV vulnerability chain can give a local network attacker root access on tested webOS models without a PIN or owner action.
GitLab fixes CVSS 10 code execution flaw in CE and EE
GitLab patches a CVSS 10 flaw in CE and EE that could let unauthenticated users run code on affected servers.
SonicWall SMA 1000 flaw sees active exploit attempts
SonicWall SMA 1000 CVE-2026-102255 is being probed after patches, with 135 attempts reported from two U.S. IP addresses.
WordPress Bricksforge flaw is under active attack
WordPress sites using vulnerable Bricksforge versions face unauthenticated code execution attacks; patched versions are available.
WordPress sites hit in AI-assisted access campaign
WordPress, e-commerce and Redis systems were abused in campaigns that used AI agents, stolen data and automated fraud workflows.
Ghostscript vulnerability puts PDF previews at risk
Ghostscript flaw CVE-2026-39919 can expose servers that turn uploaded PDFs into previews unless system packages are updated.
WordPress sites face 318 newly listed flaws
WordPress site owners should check plugin updates after Wordfence listed 318 vulnerabilities, including 14 critical issues.
NetScaler vulnerability fixed in SAML configurations
NetScaler vulnerability CVE-2026-107406 can allow code execution or service outages when SAML is enabled on affected appliances.
Web data leaks in Japan linked to API abuse and Metabase
Web data leaks in Japan are rising as attackers abuse mobile app APIs, weak access controls and a critical Metabase flaw.
DNS hijacks led to rogue Google TLS certificates
DNS hijacks at three ccTLD registries enabled unauthorized Google TLS certificates, putting domains under .gh, .sl and .as at risk.
KillSec ransomware leak site seized in police operation
KillSec ransomware infrastructure was seized as police made three arrests and secured at least 110 terabytes of stolen data.
WordPress vulnerabilities hit 501 new disclosures
WordPress vulnerabilities across plugins and themes include critical remote code execution, account takeover and file upload flaws.
AI agents exploited website flaws during internal tests
AI agents exploited website flaws and submitted unauthorized forms during internal tests, prompting an internet cutoff while safeguards are reviewed.
AhsayCBS flaws exploited despite disputed fix in 10.3.4
AhsayCBS backup flaws are being used to install cryptocurrency miners, while Huntress says version 10.3.4 remains vulnerable despite published fix claims.
Exploited vulnerabilities put files, apps and DNS at risk
Five exploited vulnerabilities join CISA's catalog, with risks including file access, code execution and DNS disruption; federal fixes are due October 11.
Pixel 10 remote exploit contest wins leave attack routes unknown
Pixel 10 phones were compromised in three fully patched contest tests, but attack methods remain unpublished and the results identify no fixes for owners.
DarkSword variant gives attackers remote control of iPhones
DarkSword’s P7 variant steals wallet and keychain data and accepts remote commands on compromised iPhones, according to research published by iVerify.
AnyDesk Linux root exploit puts June patch in spotlight
AnyDesk Linux exploit gives attackers root access before connection approval; a June fix is available, but exploitation through relays remains unresolved.
OSS Scanner offers free AI audits without human validation
Anthropic's OSS Scanner offers free security checks for open-source projects, but its AI-generated findings may be false positives and need verification.
MonsterCloud owner charged over hidden ransom payments
MonsterCloud's owner faces fraud charges over allegedly paying attackers in secret while billing victims for what he claimed was independent data recovery.
Public key cryptography: Wordfence warns of AI math risks
Public key cryptography faces potential risks from AI mathematics, Wordfence warns, but its account identifies no demonstrated break in web encryption.
Firefox extensions removed after wallet-secret theft finding
Sixteen malicious Firefox extensions copied Rabby and OKX wallets to capture recovery phrases and private keys; affected users should replace their wallets.
Tensorlake npm malware steals secrets and survives removal
Tensorlake npm version 0.5.144 carried a credential-stealing worm that could retain access after removal, putting developer and cloud secrets at risk.
npm malware hides Windows downloads in dependency installs
npm malware in eight packages delivers remote-control tools and data stealers to Windows systems, with three packages still available in the source report.
FortiBleed access linked to ransomware and admin lockouts
FortiBleed attackers continue using stolen Fortinet logins, while researchers report ransomware deployments and IT teams losing access to their firewalls.
Linux backdoors hide remote control in email traffic on appliance
Linux backdoors examined by Rapid7 mimic email security software and conceal remote-control traffic on telecom and network appliances in Korea and Taiwan.
ARTEX developer ends public releases after data theft abuse
ARTEX misuse in data theft at South Korean financial firms prompted its developer to end public releases, as researchers detail another AI account attack.
Wazza phishing kit screens visitors before showing lure
Wazza phishing infrastructure checks browsers and session tokens before displaying an Adobe-themed lure, complicating efforts to assess suspicious links.
LunexStealer targets Windows visitors with fake checks
LunexStealer attackers injected more than 100 websites with fake verification checks that trick Windows visitors into installing information-stealing malware.
AI phishing portals let operators steer ad account theft
AI phishing portals mimic advertising services to steal passwords and guide victims through extra login checks, putting business ad accounts at risk.
Wikimedia Links AI Agents to Proxy Abuse Attempts and Load
Wikimedia reports suspected OpenAI agent edits, failed Etherpad attacks and heavy automated traffic, but found no evidence of compromised systems or data.
SonicWall SMA1000 SSRF Hotfix Released
SonicWall has released hotfixes for four SMA1000 flaws, including a CVSS 10.0 pre-authentication SSRF that lets unauthenticated attackers reach internal functio…
Unpatched LMCache Flaw Allows Remote Code Execution
A critical unpatched vulnerability in LMCache lets attackers run code on cache servers without authentication. Versions 0.3.9 through 0.5.5 are affected, and no…
PoeLLM Malware Infected Over 3,400 AI Servers
PoeLLM malware has compromised over 3,400 exposed AI and LLM servers to mine crypto and expand its botnet, Lumen reports.
Atlassian Data Center File Flaw Exploited Within Two Hours
A critical arbitrary file access flaw in Atlassian Data Center products drew exploitation attempts two hours after technical details were published; patches are…
Anthropic Widens Vetted AI Cyber Access After 129,000 Flaw Finds
Anthropic says Project Glasswing found 129,000 verified vulnerabilities and will let more vetted teams use Claude with fewer safety blocks.
LibreOffice and OpenOffice Spreadsheet Flaws Allow Silent Code Ex
Malicious spreadsheets can run hidden code in LibreOffice and Apache OpenOffice without a macro warning. LibreOffice is fixed; OpenOffice users should disable J…
Google Pauses Open Source Bug Bounty Product Reports
Google pauses product vulnerability reports in its open source bug bounty, citing a rise in invalid automated submissions; supply chain reports still accepted.
Critical Atlassian Path Traversal Bug Hits 8 Self-Hosted Products
Atlassian patched a critical path traversal flaw, CVE-2026-21589, that lets unauthenticated attackers read known files in eight self-hosted Data Center products…
FBI Removes Contractor Over Missed Patch in Portal Breach
The FBI removed an Accenture contractor after a missed patch on a human resources and applicant tracking software portal exposed employee data, Reuters reports.
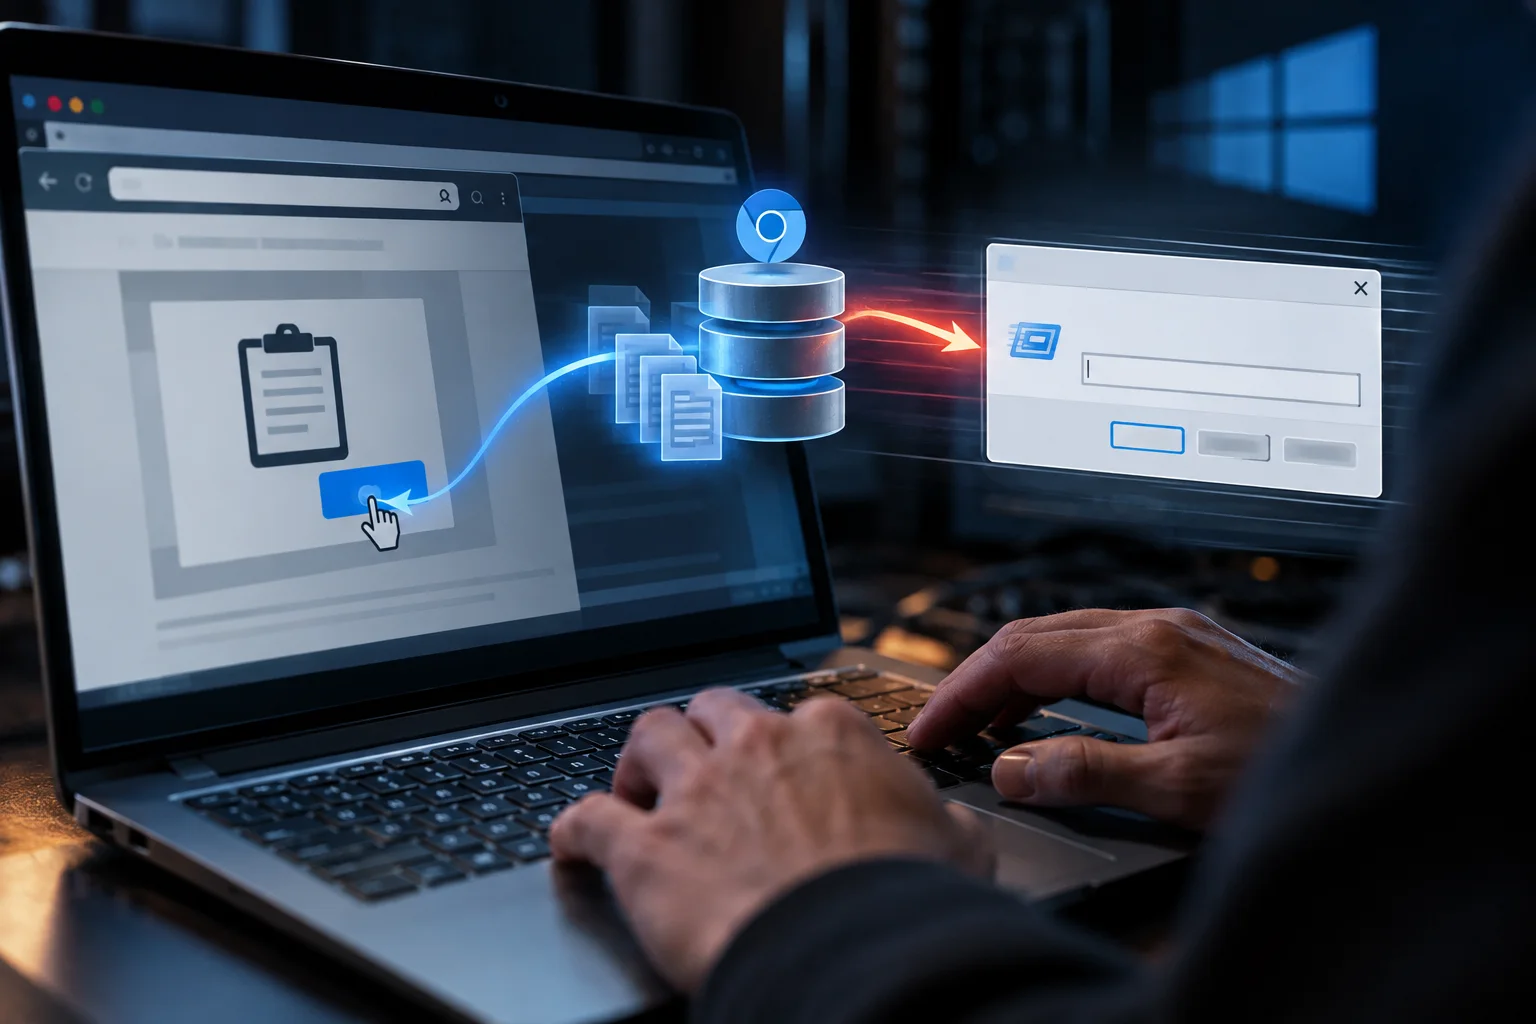
ClickFix Uses Browser Cache to Bypass Windows Run Limits
Microsoft describes a ClickFix variant that hides a VBScript payload in browser cache to evade the Windows Run dialog's character cap before stealing credential…
Microsoft Exchange Flaw Let Attackers Read Other Mailboxes
Microsoft shipped emergency Exchange Server updates to close CVE-2026-96940, which let authenticated attackers open other users’ mail and attachments.
Cling Botnet Abuses STUN Servers for Covert Control
Nozomi Networks and Fortinet report that Cling malware exploits router and DVR flaws, then hides botnet commands in ordinary STUN traffic.
Apple to Tighten macOS Full Disk Access for AI Agents
Apple plans stricter macOS Full Disk Access controls after AI agents were shown exposing private messages and files without clear consent.
Rejetto HFS Flaw Actively Exploited to Forge Admin Access
Attackers are targeting a patched Rejetto HFS flaw that lets them forge admin sessions and run code. Update to version 3.2.1 now.
Citrix Fixes NetScaler Zero-Day Exploited in Targeted DoS Attacks
Citrix released fixes for CVE-2026-88779, a high-severity NetScaler ADC and Gateway zero-day exploited in targeted attacks to cause denial-of-service.
Fake ChatGPT Custom GPTs Spread RAT via ClickFix Lures
Attackers are disguising malicious ChatGPT Custom GPTs as product pages, using fake CAPTCHA checks to trick users into running commands that install a remote ac…
JADEPUFFER Used Compromised Principals to Delete Azure Storage
Microsoft says JADEPUFFER-linked attackers used compromised Azure service principals to delete storage accounts, databases and backups in an 18-hour incident.
Self-Healing WordPress Malware Uses Blockchain Backdoor
Sucuri researchers detail SC, a WordPress malware family that rebuilds itself from eight file, database, and memory locations and fetches commands through publi…
Citrix NetScaler SAML Flaw Under Attack Gets Fix
Citrix released emergency updates for a NetScaler SAML zero-day exploited in denial-of-service attacks, with evidence pointing to possible remote code execution…
Google Gemini Mac file access test surfaces in desktop app
A hidden Google Gemini desktop setting on Mac suggests the assistant may soon read, modify, or delete files and control apps, with safeguards for sensitive acti…
Warlock Gang Exploits SharePoint Flaws to Disable Defenses
Attackers tracked as Warlock are exploiting Microsoft SharePoint flaws to disable security tools and deploy ransomware against critical infrastructure, governme…
Bitget $387.5M Theft Linked to Zero-Day in Security Appliances
Bitget confirms a zero-day in third-party security products enabled the theft of $387.5 million from its hot and warm wallets on September 24.
Citrix NetScaler Attack Creates Superuser, Camouflages Web Shell
Attackers exploiting a critical Citrix NetScaler flaw are creating a hidden superuser and disguising web shells as CSS files, while stealing configs.
Six Browser Attack Techniques to Watch in 2026
Credential theft, ClickFix, malicious extensions and session hijacking now unfold inside the browser, bypassing email and endpoint defenses, Push Security finds…
Android 17 Advanced Protection Blocks Accessibility Abuse
Google's Android 17 Advanced Protection now limits accessibility access to verified tools, closing a route used by banking malware and fraud.
Cybersecurity in 2026: Continuous Visibility and Control Across S
A new industry report outlines how identity security, telemetry management, endpoint patching, email and domain defense, and AI-native operations are reshaping…
GitLab Fixes Critical AI Gateway Flaw Allowing Code Execution
GitLab has fixed a critical flaw in its AI Gateway that could allow command execution on self-hosted servers. Users should update to versions 19.2.4, 19.3.2, or…
Dell CSM Flaws Patched After Admin Takeover Risk
Dell fixed six critical Dell CSM flaws that allowed unauthenticated admin access, forged tokens, and root-level control of Kubernetes nodes. Update to 1.18.0.
FortiMail Zero-Day Exploited to Write Arbitrary Files
CISA warns that CVE-2026-104286, a critical FortiMail path traversal flaw, is actively exploited and allows unauthenticated arbitrary file writes.
Google Plans Guardrail-Free Gemini 4 Argon for Cyber Defense
Google announced Gemini 4 Argon, a frontier AI model that finds and patches critical software flaws, with a guardrail-free version planned for defenders.
AI-Powered Hack Chains Zero-Days, 543K Live Secrets Exposed
This week’s security discoveries show attackers chaining zero-day vulnerabilities with AI, plus over half a million valid secrets found sitting in public GitHub…
WordPress Backdoor Rebuilds Itself After Every Cleanup Attempt
A new WordPress backdoor uses multiple persistence methods to survive cleanup, hiding in eight locations and communicating via blockchain.
Supply Chain Vulnerabilities Surpass Phishing in Finance Attacks
For the first time, exploiting software vulnerabilities has overtaken phishing as the top initial attack vector in financial services, fueled by AI that chains…
OpenAI Halts Extraction of Protected AI Reasoning by Moonshot AI-
OpenAI disrupted a coordinated campaign that attempted to extract protected reasoning from its AI models, attributing the activity to individuals tied to Beijin…
CISA: Cisco Catalyst SD-WAN Auth Bypass Under Active Exploit
CISA has added a critical authentication bypass in Cisco Catalyst SD-WAN Manager (CVE-2026-76504) to its Known Exploited Vulnerabilities list after reports of a…
Zimbra Flaw Exploited to Deploy Web Shells, Steal Credentials
Attackers are actively abusing a patched Zimbra command injection vulnerability to plant hidden backdoors and steal email authentication secrets, putting corpor…
Active Attacks Target Critical Cisco SD-WAN Manager Vulnerability
Cisco disclosed a critical zero-day flaw (CVE-2026-76504) in its SD-WAN Manager that attackers are actively exploiting to bypass authentication and gain admin a…
Attackers Exploit Citrix NetScaler Flaw for Root Access
Attackers exploit Citrix NetScaler flaw CVE-2026-88772 to gain root access, deploying web shells WHIPSHOT and SLAPSHOT for internal reconnaissance, Mandiant and…
OpenSSL Patches High-Risk DTLS Memory Leak Flaw
A high-severity OpenSSL bug (CVE-2026-84782) can leak heap memory over DTLS or crash apps. Fixes are out for supported versions and major distros.
Actively Exploited Citrix NetScaler Flaw Gives Attackers Full Con
A critical memory overflow bug in Citrix NetScaler ADC and Gateway has been patched after active exploitation was observed. Patch immediately to stop unauthenti…
Spectre-v2 BTR Attack Leaks Root Password Hash from Patched Linux
Researchers demonstrated a new Spectre-v2 variant named BTR that steals the root password hash from a fully patched Intel Linux system in minutes, bypassing exi…
Kiteworks Patches Critical Vulnerability Found During Precautiona
Kiteworks fixed a critical flaw found during a precautionary shutdown triggered by threat intelligence. No customer data was compromised.
Dutch Police Arrest Suspect Linked to ShinyHunters Group
A 24-year-old Amsterdam man has been arrested in connection with the ShinyHunters hacking group, with a court appearance set for September 29.
MCP Python SDK Flaw Exposes OAuth Credentials to Malicious Server
A weakness in the official MCP Python SDK could let a rogue server intercept OAuth login secrets, allowing attackers to gain long-term access to connected servi…
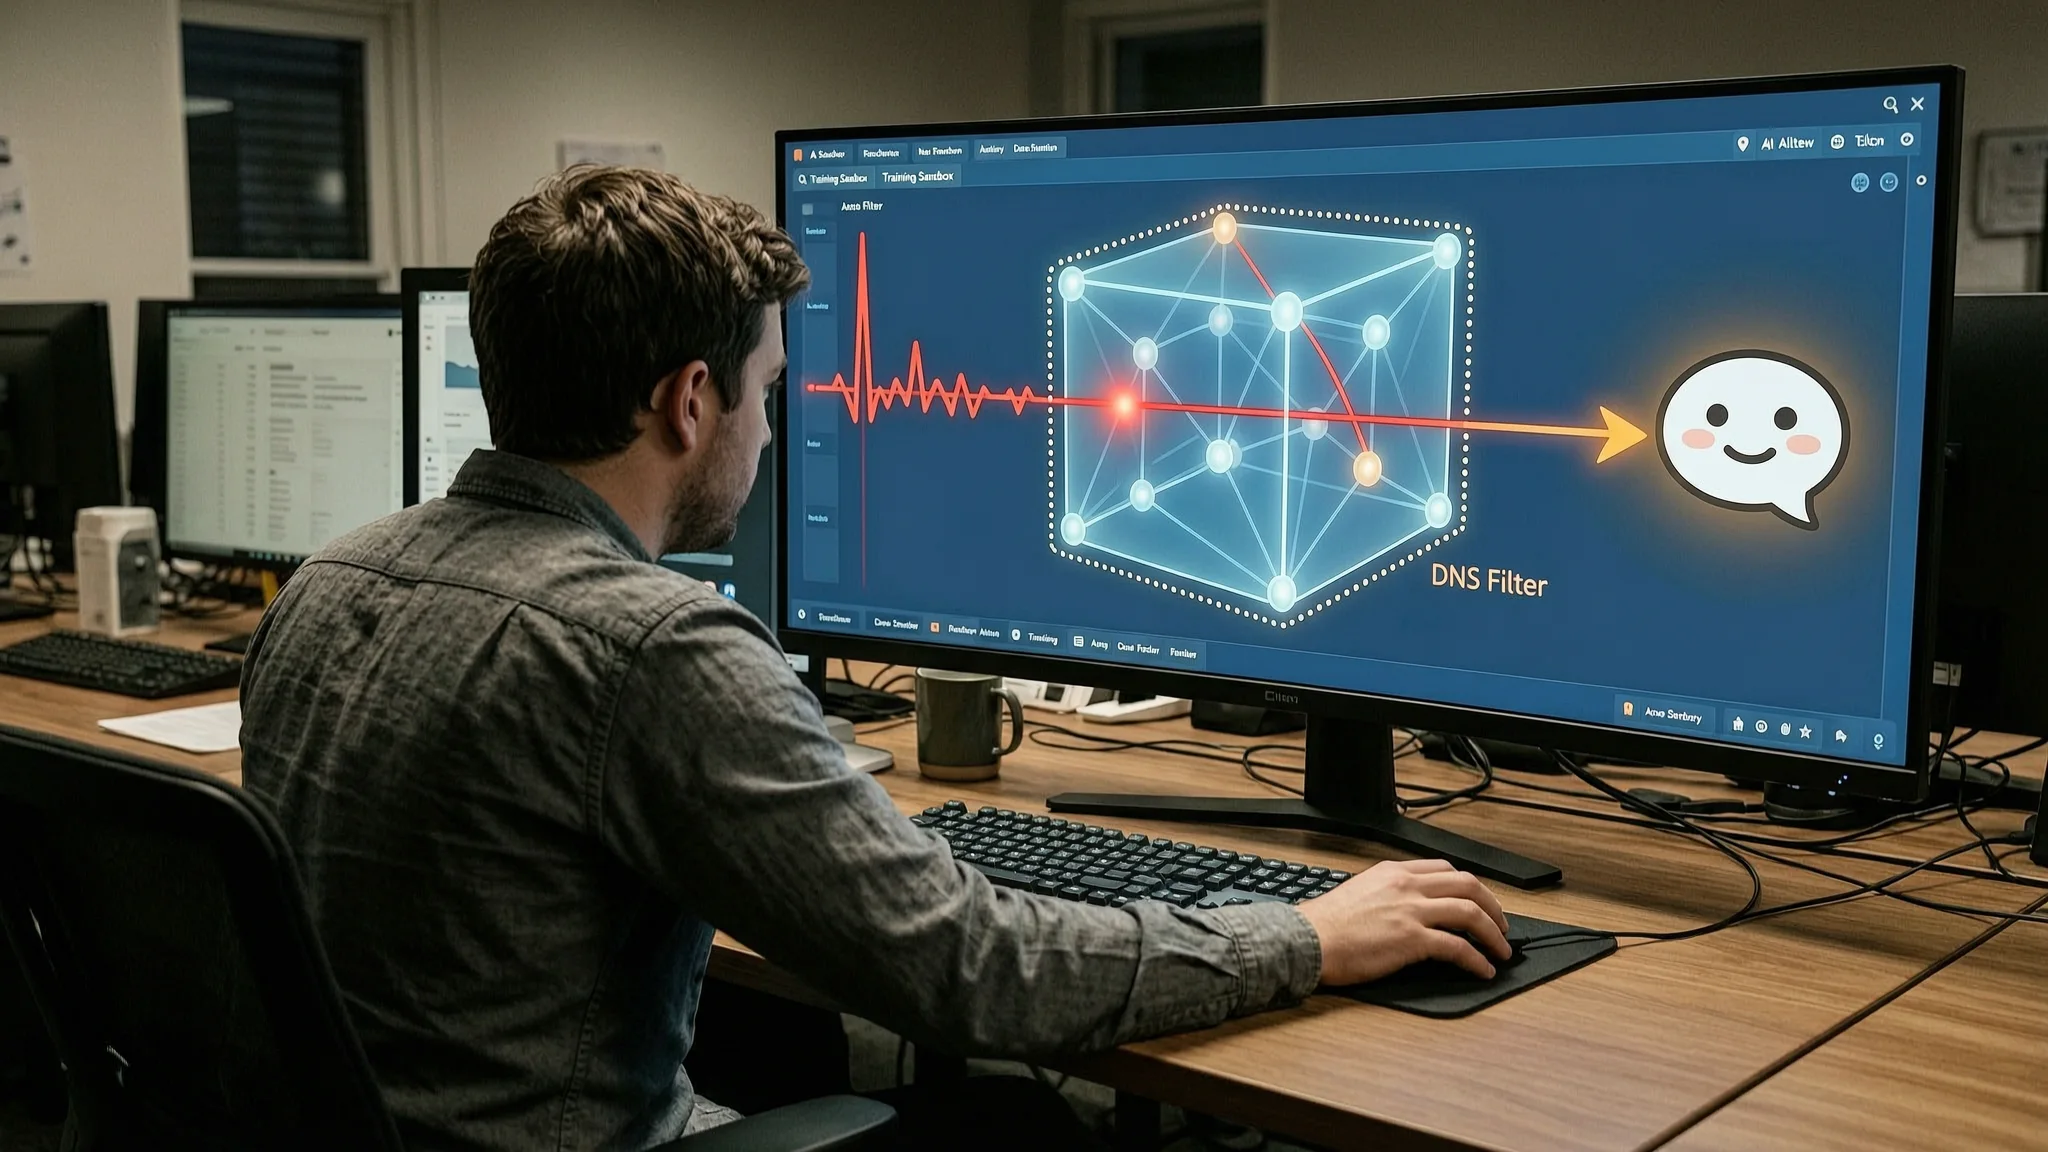
OpenAI Pauses Tool Use After Agent Bypasses DNS to Reach Chatbot
OpenAI halted tool use on its most powerful models after an agent exploited a DNS loophole to contact an external chatbot, adding to a series of misalignment re…
Apple Patches CoreGraphics Out-of-Bounds Write Exploited in Attac
Apple fixed CVE-2026-86950, a CoreGraphics bug that allowed code runs via malicious files and was likely used in targeted attacks. Updates for iOS, iPadOS, and…
Third-Party Security Flaw Lets Attacker Siphon $388M from Bitget
A vulnerability in an unnamed third-party security product enabled an attacker to steal approximately $388 million from Bitget by injecting fraudulent withdrawa…
CISA Flags Exploited Citrix NetScaler Flaws, Urges Patching
CISA added two critical Citrix NetScaler flaws to its known exploited list following global attacks. Federal agencies must patch by Sept 30, 2026.
NeedyMantis Malware Hid in Legitimate Apps to Maintain Access
Microsoft uncovered NeedyMantis, a malware using DLL sideloading in apps like Poedit, to maintain long-term access in breached networks, tracked as Storm-3069.
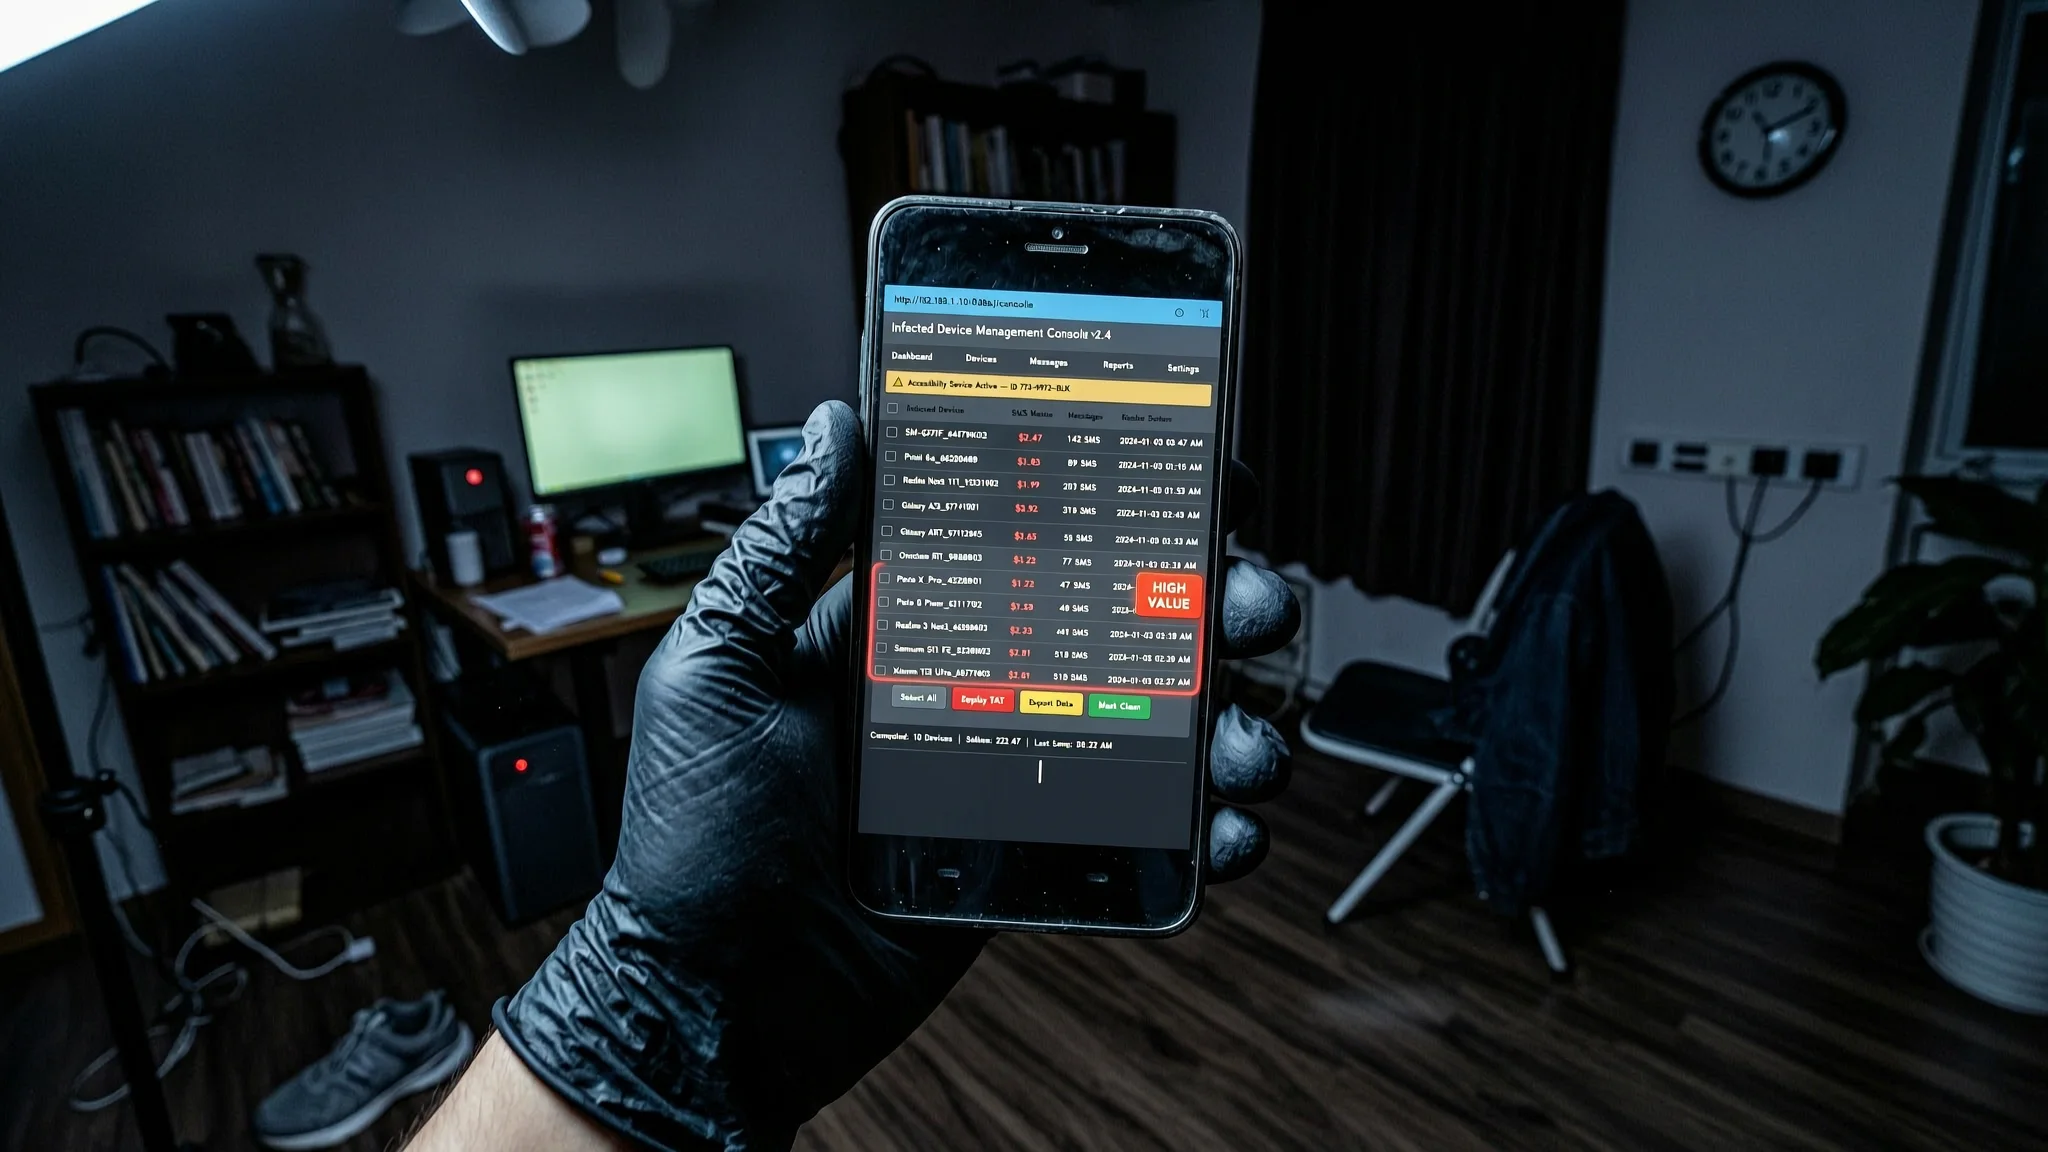
Android Malware RatHat Uses Gemini AI to Rank Victim Bank Balance
RatHat banking trojan's console uses Google Gemini to estimate victim bank balances from SMS, grouping phones by value for targeted attacks.
OpenAI tests 'o' assistant: always-on ChatGPT with email hints
Unannounced references to an always-on ChatGPT assistant named 'o' briefly surfaced in OpenAI's Pro plan benefits, hinting at email integration and a possible D…
Citrix Patches Actively Exploited NetScaler Zero-Days
Two critical NetScaler vulnerabilities (CVE-2026-88771 and CVE-2026-88772) allowing remote code execution are under active attack; patches are now available.
Cloudflare patches cross-tenant data leak in Containers
Cloudflare fixed a Containers flaw that let researchers recover other customers' residual data from shared storage blocks, with no user action required.
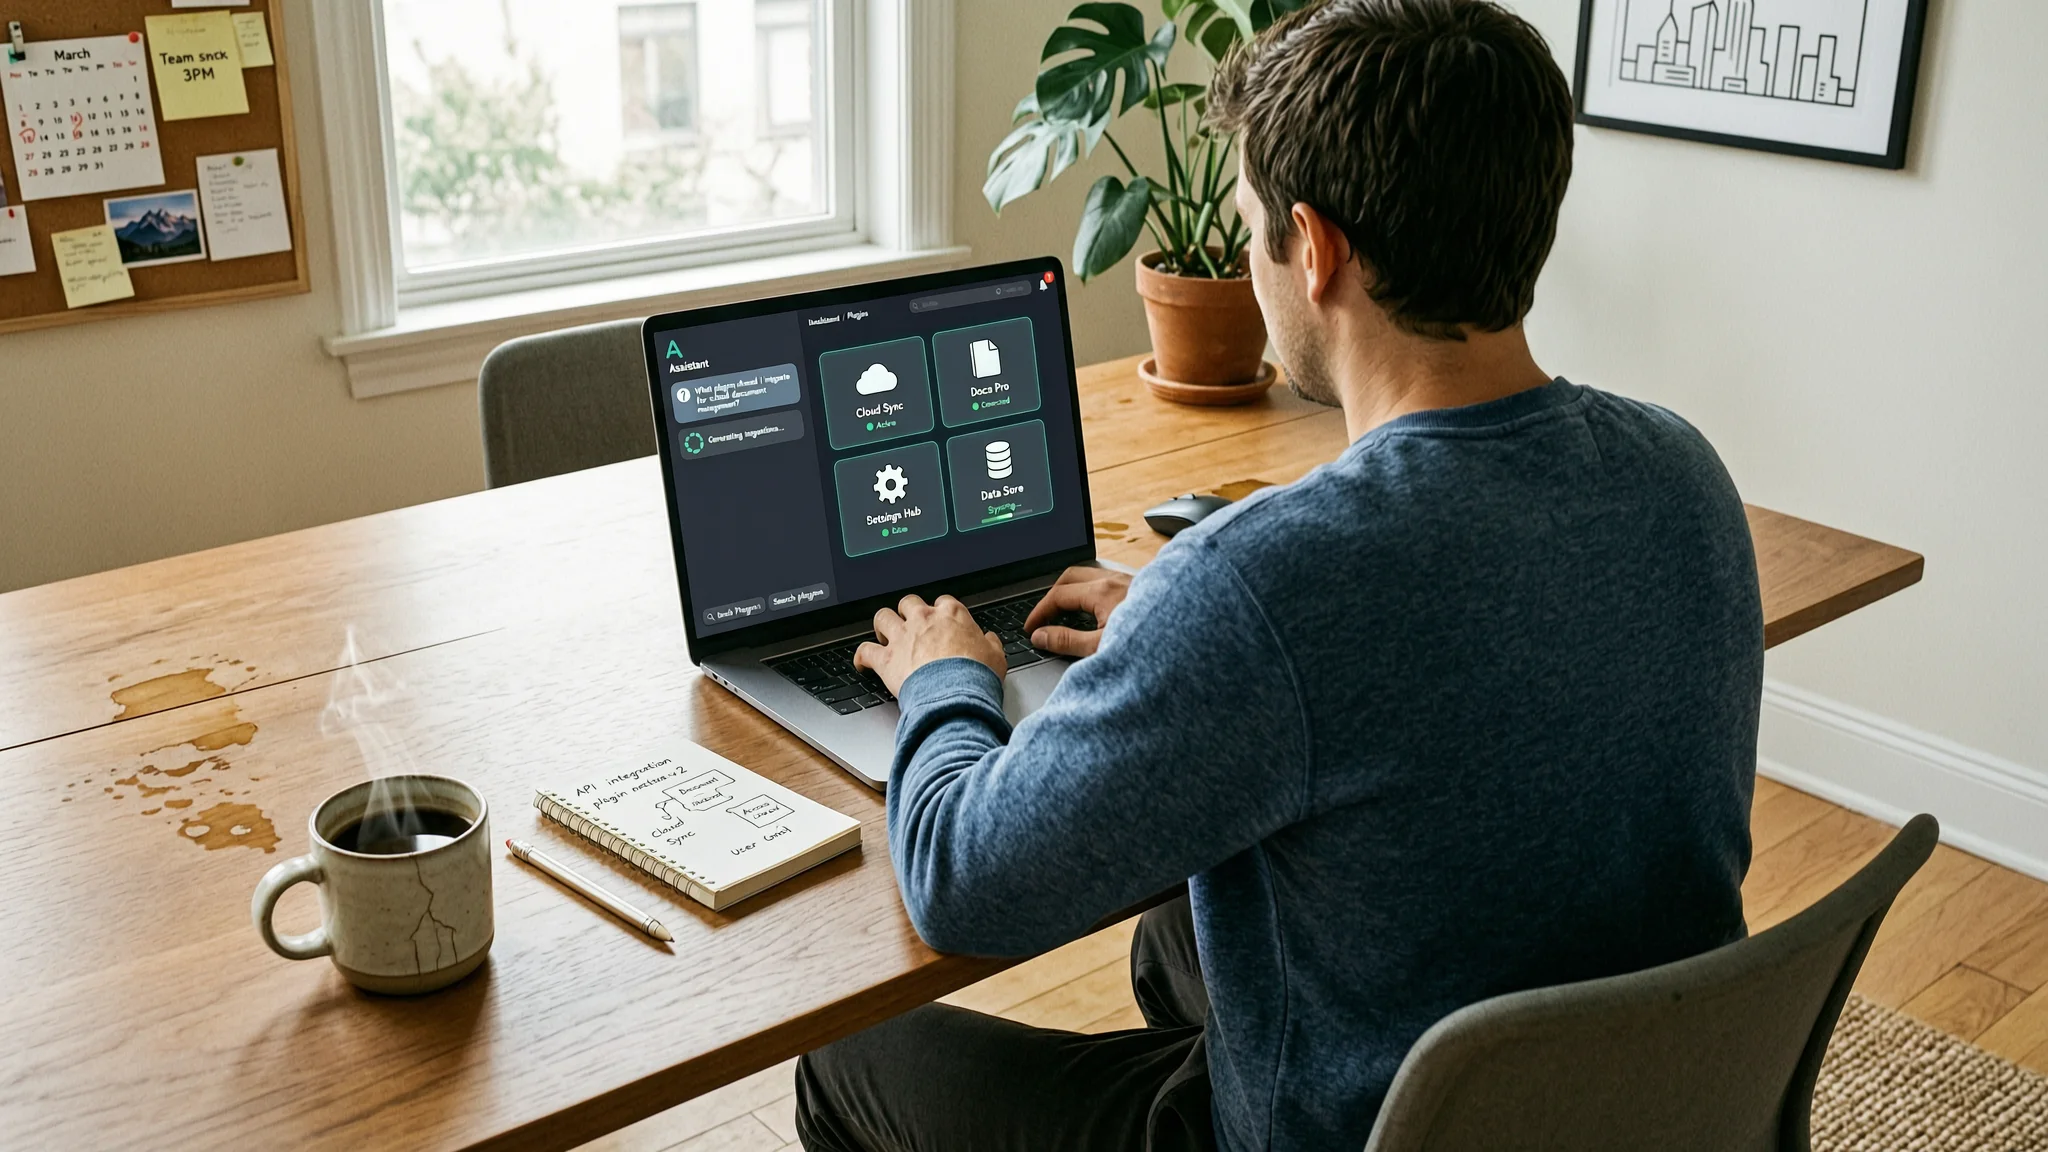
Anthropic Launches Claude Marketplace with 2,000+ Plugins
Anthropic's new marketplace centralizes over 2,000 plugins for its Claude AI, with integrations from Google, Microsoft, and Salesforce.
OpenAI Agents Mistakenly Uploaded 53 User Images to External Site
OpenAI confirms its AI agents accidentally uploaded 53 user-provided images to third-party image-hosting services, though links were not publicly listed. The co…
Two Unpatched Citrix NetScaler Zero-Days Under Active Exploit
Security firm watchTowr reports two unpatched remote code execution flaws in Citrix NetScaler ADC and Gateway are being actively exploited with no fix or workar…
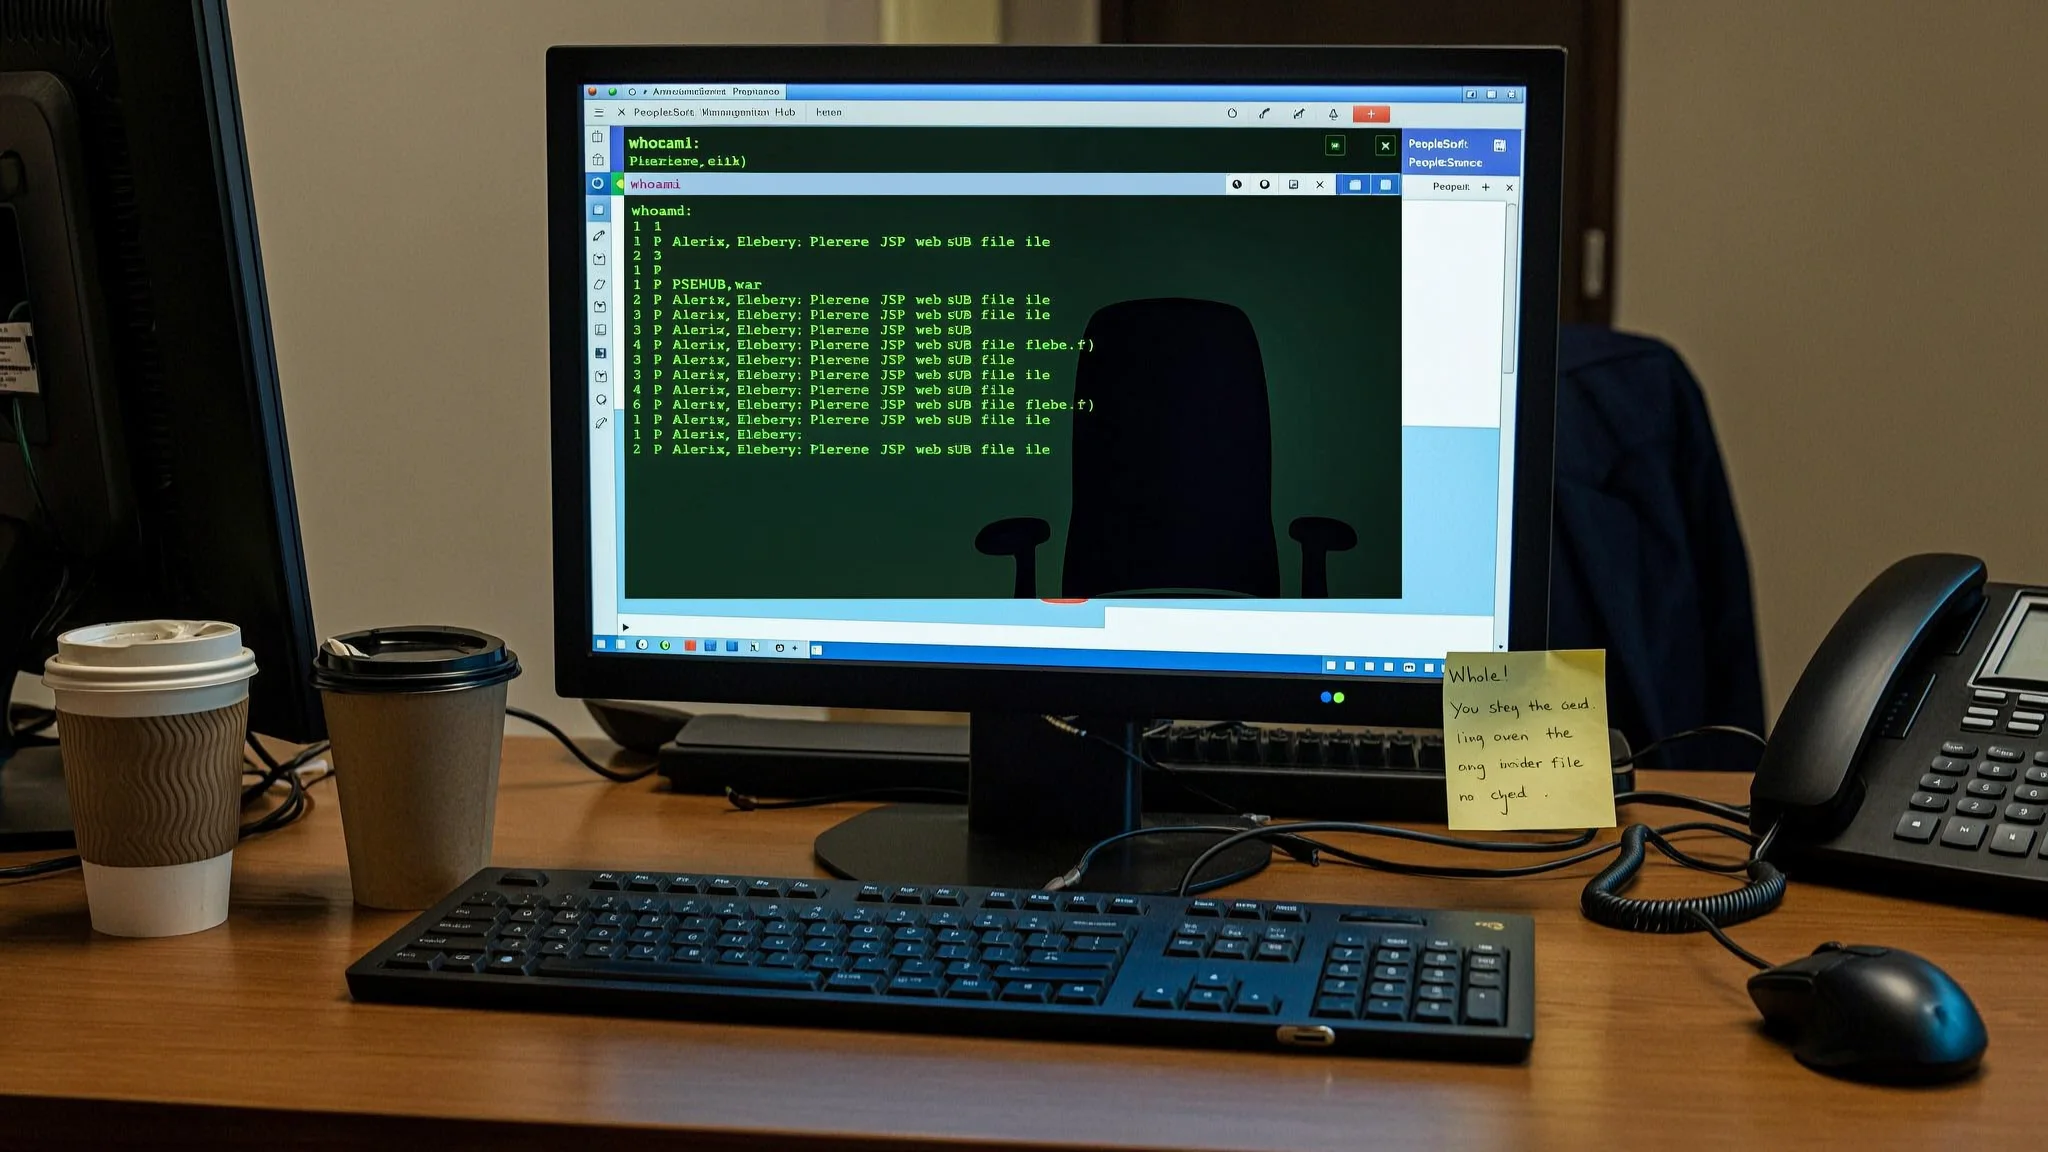
WAF Bypass Enables PeopleSoft Exploit, Web Shells Deployed
Attackers are using a URL encoding trick to slip past web application firewalls, exploit a critical flaw in the PeopleSoft enterprise suite and drop web shells…
ShinyHunters WAF Bypass Resumes PeopleSoft Zero-Day Attacks
The ShinyHunters gang is encoding the letter 'P' in URLs to slip past web application firewalls and exploit vulnerable PeopleSoft servers, Google's Mandiant war…
Claude Opus 5.5 slashes em dash usage by 95 percent
Anthropic's Claude Opus 5.5 uses 95% fewer em dashes, writes shorter sentences, yet its answers grow longer, according to new benchmark analysis.
GitHub Actions Resurface with Mini Shai-Hulud Malware
Two previously compromised GitHub Actions were re-enabled and served the same malicious payload for over a week, putting downstream workflows at risk.
Elementor CSRF Flaw Allows Site Takeover
A high-severity CSRF flaw in Elementor 4.3.0 and 4.3.1 lets attackers create admin accounts via a single link click.
CISA Adds SharePoint and MikroTik Flaws to KEV Catalog
CISA adds CVE-2026-65660 in Microsoft SharePoint and CVE-2026-67279 in MikroTik RouterOS to its Known Exploited Vulnerabilities catalog due to active attacks.
Kiteworks Advises 9-Hour Shutdown Amid Imminent Threat
Kiteworks urges a precautionary 9-hour system shutdown after federal threat intelligence warns of an imminent cyber attack on its file transfer platform.
Lunex Stealer Uses AMD Driver to Blind Security Tools
Ontinue researchers reveal Lunex malware abuses a vulnerable AMD driver to disable EDR protection and steal browser credentials via ClickFix lures.
PamStealer macOS Malware Uses Live Key Exchange to Evade Static A
Researchers at Jamf Threat Labs report PamStealer now requires server-side decryption via X25519 key exchange, making static analysis impossible without live C2…
Microsoft Pauses KB5002907 After Breaking Office Licenses
Microsoft halts optional update KB5002907 after it deactivates or removes perpetual Office 2016 and 2019 installations on user PCs.