
PHP2Shell patch is the only reliable fix for PHP flaws
PHP2Shell covers two critical PHP remote code execution (RCE) flaws, meaning weaknesses that could let an attacker run commands on a vulnerable web server from elsewhere. PHP rates both flaws at 9.2 out of 10 and scheduled fixes for 14:00 UTC on October 21. As of the reporting period, those fixes had not yet been released, and PHP had not disclosed the affected versions, the vulnerable component or any configuration-based workaround.
That lack of technical detail means administrators cannot yet prove that a particular defensive setting blocks PHP2Shell. Cloudflare reported early exploitation attempts and deployed emergency filtering rules, including for its free tier, but described those rules as temporary protection until systems can be patched. No successful compromise had been confirmed, circulating public exploit code had not been demonstrated to work, and neither flaw appeared in the US Cybersecurity and Infrastructure Security Agency catalog of known exploited vulnerabilities when checked on October 21. Separately, watchTowr said it reproduced one flaw but had not reported attacks.
The most widely shared proposed mitigation is session.upload_progress.enabled=0, which disables PHP's Session Upload Progress feature. That feature is enabled by default and records the progress of a file upload so another request can check it. GMO Flatt Security initially suggested disabling it might help, while warning that it could not confirm complete protection. In an update timestamped 14:00 Japan time, or 05:00 UTC, the firm clarified that the setting alone was insufficient and said attackers were expected to be able to bypass it. Members of the PHP project likewise stated that changing INI configuration settings cannot replace patching or upgrading PHP.
There is also no public confirmation that Session Upload Progress is where either vulnerability resides. GMO Flatt Security tied its advice to its own assessment of what PHP2Shell might involve. An anonymous code audit disputed the claimed flaw in that feature and said the circulating proof-of-concept did not work against released PHP. Upwind continued to list the setting as an immediate mitigation based on another researcher's analysis, while watchTowr said there was no confirmed workaround. PHP's eventual advisory and code changes are needed to settle the disagreement.
Administrators who have already disabled upload progress do not need to reverse the change, but they should not treat it as a security fix. PHP's manual already recommends disabling the feature when an application does not need upload progress bars because stored file and form-field names are not validated and may contain PHP code. Disabling it on a site that requires the feature will stop its upload progress bars from working.
The setting must also be changed in the PHP process that actually handles website requests. It is an INI_PERDIR option and can be configured through php.ini, .htaccess or .user.ini. The .user.ini method applies only to CGI and FastCGI deployments, not the Apache module, and PHP checks that file every 300 seconds by default, so a change can take five minutes to become active. Sites using the Apache module need .htaccess or server configuration. Checking php -i at a command line does not confirm the value used by PHP-FPM or mod_php for web traffic.
Administrators able to update promptly should prepare their deployment procedure, post-update checks, approvals and any necessary restart before the release. The component to update is the PHP runtime serving web requests, such as PHP-FPM, mod_php or CGI, rather than WordPress, Laravel or another application running on top of it. PHP currently provides fixes for four supported branches, 8.2 through 8.5. The precise fixed releases and the full range of affected versions were due to be published with the advisory.
Sites that cannot patch immediately should reduce their exposure. CERT-EU advises considering isolation of internet-facing applications from public networks until a fix is available. Practical options include temporarily taking a site offline or placing it behind authenticated access, a VPN or an allowlist of approved clients. Administrators must also prevent visitors from bypassing those controls and reaching the origin server directly. GMO Flatt Security additionally recommends reducing stored data and server privileges, removing saved credentials and cloud roles, and preserving logs in a secure location for later investigation.
Unsupported PHP branches older than 8.2, including 8.1, 7.x and 5.x, do not receive fixes directly from PHP. Those systems need an upgrade, isolation or removal from the internet, although a Linux distribution or hosting provider may issue a backport, which applies a security correction without changing to a newer major version. CloudLinux said its packages depended on PHP publishing the upstream release and would follow when ready.
Another proposed stopgap is to reject requests containing a multipart/form-data body at the web server before PHP processes them. This targets the suspected request format involved in the flaws, but it remains unconfirmed. Blocking only POST requests is insufficient because PHP 8.4 introduced request_parse_body(), which can process multipart bodies sent with other methods. A broader block will interrupt file uploads and forms that use multipart data even when no file is attached.
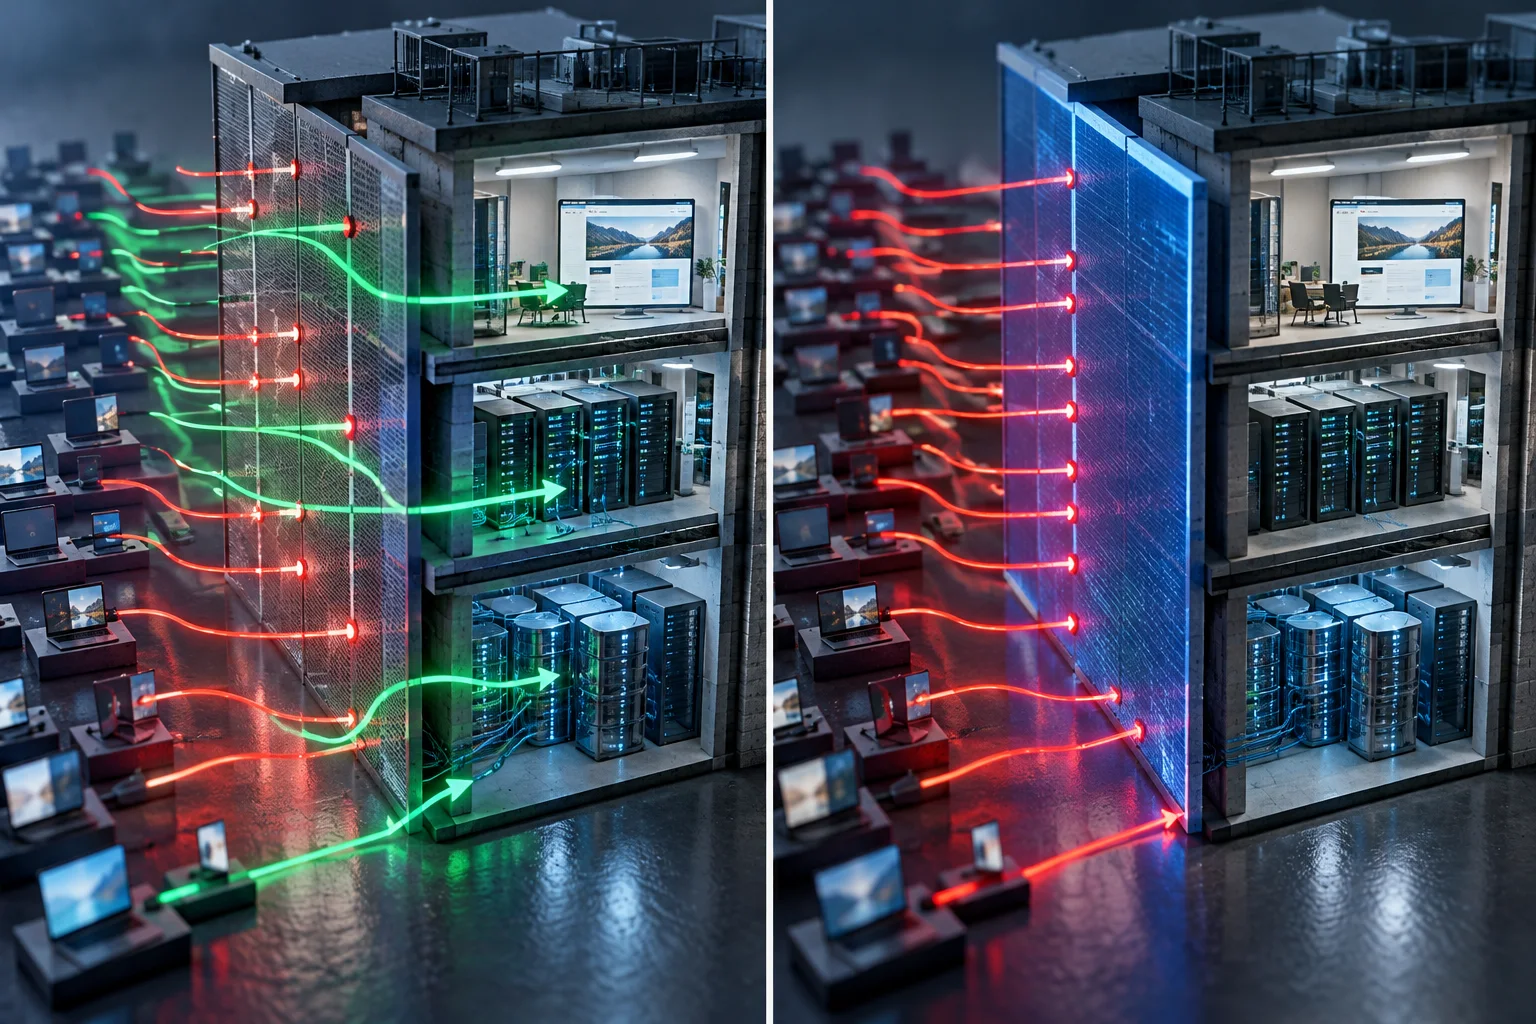
A web application firewall can filter known malicious request patterns, but it is not a replacement for the PHP2Shell patch. Cloudflare's rules only inspect requests routed through its service, cannot protect an origin that remains directly reachable and may miss new attack paths. For WordPress site owners reviewing their hosting arrangements, AEU Hosting offers managed WordPress hosting, secured end to end.
Managed and shared-hosting customers should ask their provider when the corrected PHP package will be installed. Linux distributions such as Debian and Ubuntu may retain an old-looking PHP version while backporting the correction, so the visible version string alone may not establish whether a server is protected. Administrators should compare the complete package version with the distribution advisory or inspect its changelog. After updating, they should confirm the fixed release for their branch through php.net or PHP's GitHub security advisories, verify what versions PHP identifies as affected, and review logs for suspicious activity that occurred before patching.