
AI phishing portals let operators steer ad account theft
AI phishing portals mimic advertising services to steal passwords and guide victims through extra login checks, putting business ad accounts at risk.
AI phishing portals are letting human operators guide victims through fake sign-in screens to steal advertising account credentials and additional login codes, according to research by Island. The operation impersonates advertising services associated with Google Gemini, Anthropic Claude, OpenAI ChatGPT, Perplexity, Meta Muse and Manus. For businesses and website owners buying online advertising, the target is an account that controls campaigns, spending and potentially access to clients.
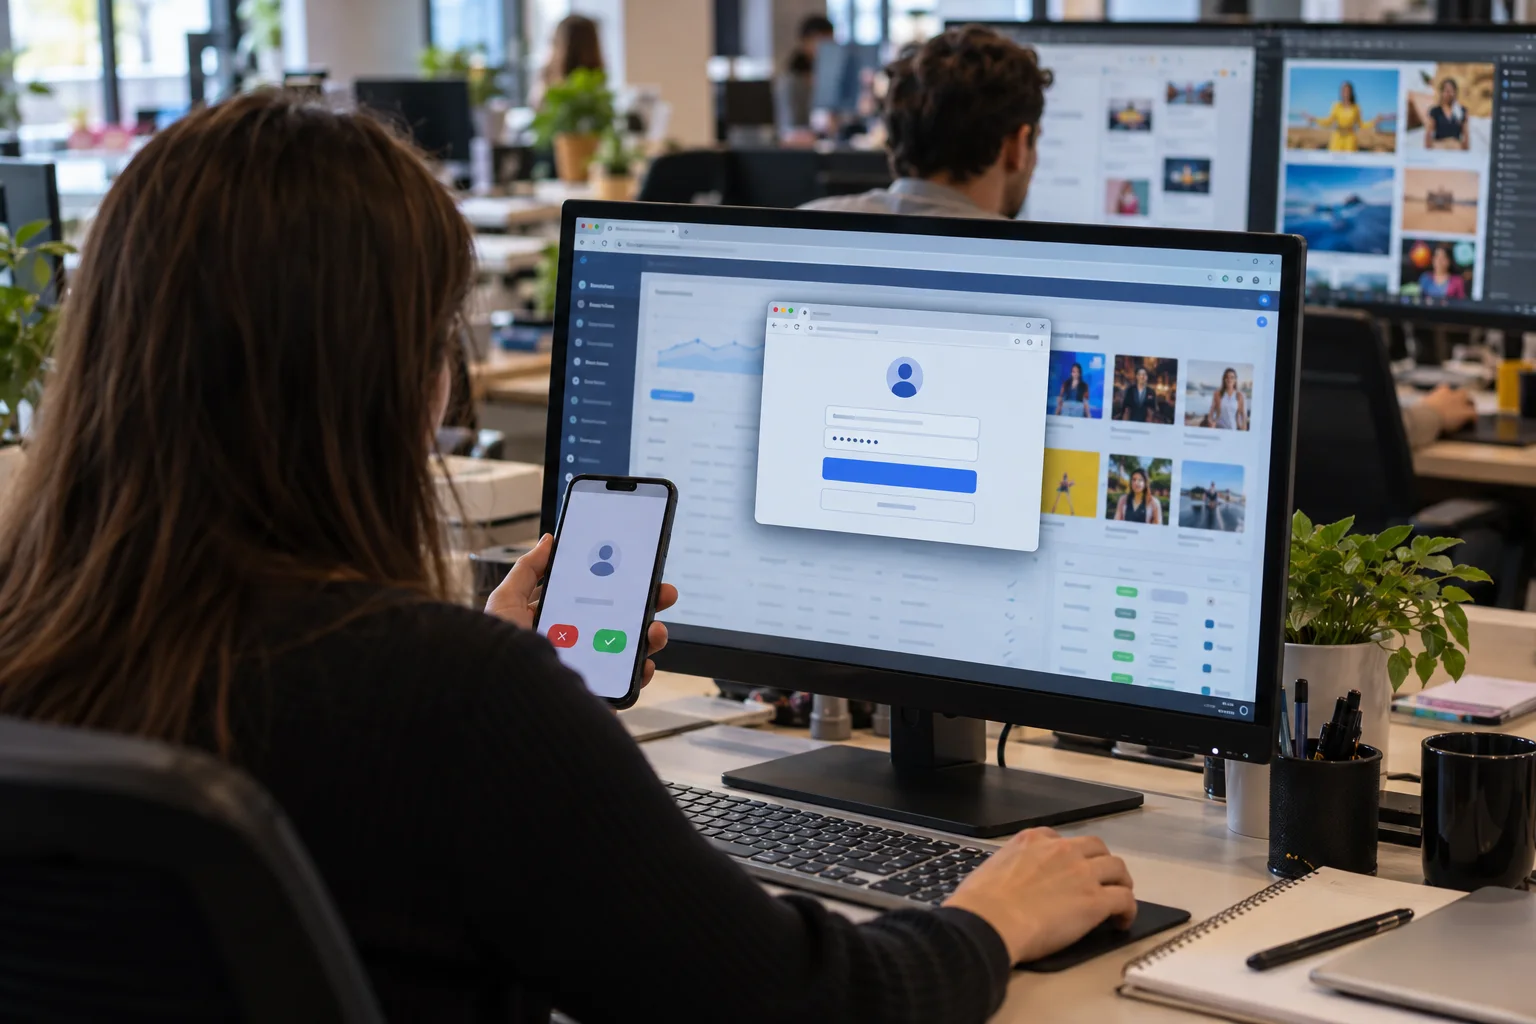
Island researchers Oleg Zaytsev and Ofek Ronen described the platform in a report shared with The Hacker News. Its central deception is browser-in-the-browser (BitB), a technique that draws a counterfeit browser window inside a web page. The imitation includes an address bar showing a trusted sign-in address, such as accounts.google.com or an Okta tenant, an organisation’s dedicated identity-service environment. The real browser, however, never leaves the attacker’s website.
One example, museads.ai, appeared on September 16, 2026, a little over a week after Meta introduced Muse, its AI agent for personal workflows. The site presented itself as an advertising manager that could connect ad accounts, reach prospective buyers and arrange sponsored placements. A prominent prompt-entry box contained a Connect button. Selecting it launched an imitation login window for Google, Meta, TikTok or Okta workflows rather than a genuine account connection.
Behind these screens, the platform retained every password attempt and fingerprinted the visitor’s device, collecting characteristics that help distinguish it. Device information went to /api/send/ip, a server address used to receive data, over Socket.IO, software for live communication between a page and a server. Once credentials arrived, an attacker tried them against the real account immediately. The operator could then choose which multi-factor authentication (MFA) challenge, an additional identity check beyond a password, the victim should see.
Two Socket.IO events, operator-command and telegram-command, carried instructions to the page. Zaytsev, Island’s Lead Security Researcher, told The Hacker News that the inspected code routed both through the same command interpreter, rather than providing separate sets of actions. Operators could watch the victim’s progress and adjust the deception to match the genuine sign-in process they were attempting elsewhere.
The controls were extensive. The /password command requested another password; /2fa and /authApp displayed text-message or authenticator-app challenges. Google approval, QR-code verification and number-matching screens were available through /googlePrompt, /googleQrVerify and /verifyTap. QR codes are scannable square patterns, while number matching asks someone to confirm a matching number during sign-in. Okta-specific steps used /oktaUsername, /oktaPassword, /oktaSms2fa, /oktaApprove, /oktaAuthApp and /oktaVerifyTap for username, password, text-message, approval notification, authenticator and number-matching screens. Operators could reject a code with /wrong2fa, leave a visitor waiting, or finish or suppress the process with /done and /ban. These are controls over the fake interface, not evidence of a software flaw in those identity services.
Each AI phishing site had a different sales pitch. The ChatGPT impersonation offered a Monday Google Ads briefing; the Gemini version advertised MCC (manager account) support and linked client accounts. Claude had a supposed advertising portal, Perplexity offered campaign planning and spending audits, and Manus promoted a private Meta integration. The researchers assess that forged invitation emails impersonating these brands brought people to the sites, but the source does not establish that delivery route as confirmed.
Island linked the AI advertising pages to a broader platform with two other branches: Google Ads refund and payment-confirmation lures, and recruitment sites impersonating Tesla, Louis Vuitton, Nike and Adecco. All identified sites used Next.js, software for building web applications, alongside Socket.IO, and contacted the same server endpoints. Misconfigured public GitHub repositories, online storage locations for software projects, also exposed source code from earlier platform versions.
The apparent targets are agency employees, media buyers and administrators of manager accounts that oversee multiple advertising accounts. Island assesses that the likely objective is to run attackers’ advertisements or sell the stolen accounts, particularly those with a clean spending history. That motive is an assessment, not a confirmed outcome for every victim. A July 2026 Mimecast report described VietCredCare, DuckTail, NodeStealer and PXA Stealer as malware families contributing to large-scale advertising account theft, with criminals consuming business budgets and trading reputable accounts in underground markets.
Island warned that removing a payment card can be much quicker than recovering control. According to the company, attackers commonly appoint their own administrators and reduce the legitimate owner’s permissions. Recovery can take weeks or months while advertisements continue running, and a compromised manager account can expose an agency’s clients to the consequences. This makes account permissions and changes to advertising controls important checks, not just card charges.
In a separate disclosure, Island described abuse of Google-sponsored search results to send visitors to custom GPTs, customised AI assistants, or shared AI chat content. Those pages redirected users to counterfeit Cloudflare verification screens carrying ClickFix lures, deceptive instructions that persuade people to perform actions that install malware. The payload was NetSupport RAT, a remote-access tool used to control a computer. Island said this chain exploited trusted platforms, attacker-written content, paid search and social engineering, rather than a vulnerability in ChatGPT or Google. Across a three-month observation period ending in August 2026, the broader delivery cluster contained about 850 paid-ad landings, 26 lookalike ChatGPT destinations and 71 Google Ads campaign IDs.
For the advertising-account campaign, the recommended defences are phishing-resistant authentication, designed to prevent fake sites from collecting reusable sign-in proof, reviews of advertising control changes, and careful checks before connecting an AI integration. AEU-I’s security-first IT and consulting services are relevant to businesses reviewing these account-access practices. The immediate lesson is to verify the service and the real browser address before connecting a business account, rather than trusting the address drawn inside a convincing login panel.
How to Protect Yourself
- Open your advertising provider from a saved bookmark instead of an invitation email before connecting a new AI service.
- Check the address at the very top of your browser, not an address shown inside a login box on the page.
- Choose a passkey or security key in your account’s sign-in settings when the provider offers one.
- Review the people who can manage your advertising account and remove access you do not recognise.
- If you entered a password on a suspicious portal, change it through the genuine provider and check your campaigns and spending.
- Do not copy commands into your computer or run downloads because a verification page tells you to.
Terms Explained
- browser-in-the-browser (BitB) A deception that puts a fake browser window inside a website to make a false login look genuine.
- multi-factor authentication (MFA) A sign-in process requiring an extra identity check as well as a password.
- Socket.IO Software that lets a website and its server exchange information immediately while the page is open.
- manager account An advertising account used to oversee several other advertising accounts.
- ClickFix A scam that tells users to perform a supposed fix or verification step that actually helps install harmful software.
- phishing-resistant authentication A way of signing in designed to stop imitation websites from obtaining proof they can reuse to access your account.