
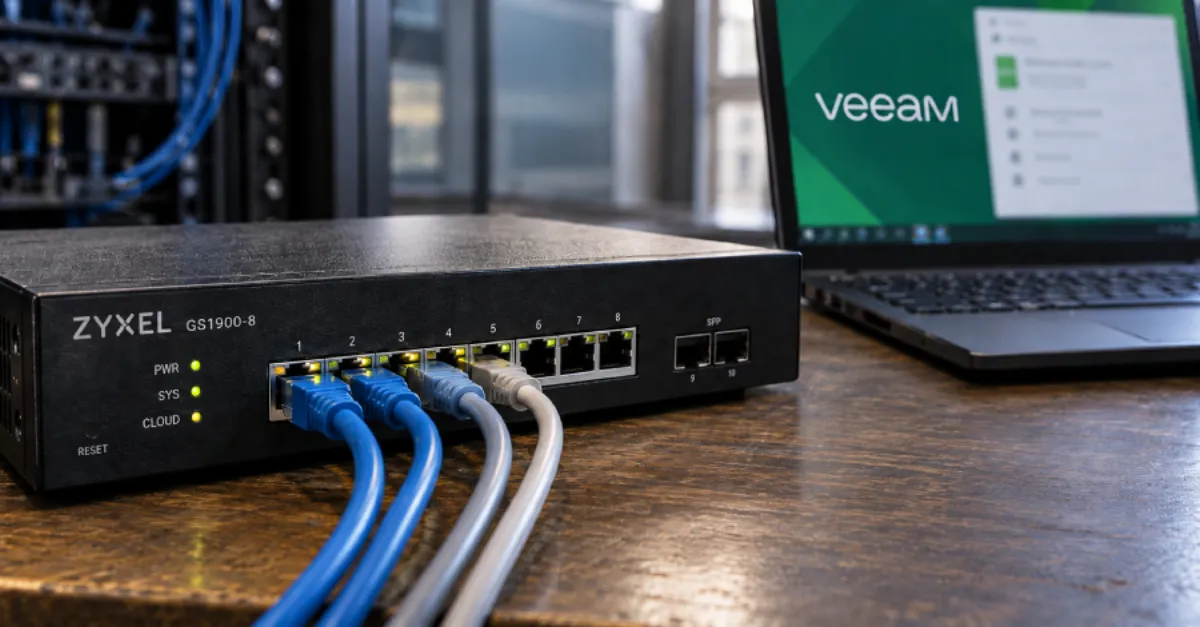
Zyxel switch and Veeam Agent flaws exploited in attacks
CISA added a patched Zyxel GS1900 switch flaw to its exploited list after 996 devices were hit, and a Veeam Agent bug is also under attack.
CISA has added a Zyxel GS1900 series switch flaw to its Known Exploited Vulnerabilities (KEV) catalog, a public list of security bugs that attackers are known to use against real systems. The flaw is tracked as CVE-2026-7273, the identifier given to one specific catalogued vulnerability, and it carries a CVSS score of 8.8 on the usual 1 to 10 severity scale, which puts it in the high severity range. The U.S. Cybersecurity and Infrastructure Security Agency made the addition on Monday and cited evidence of active exploitation. The bug has already been fixed by Zyxel, the vendor whose equipment is affected.
The issue is a stack-based buffer overflow. In ordinary language, that means the switch's software is tricked into writing more data into a small reserved space in its memory than that space can hold, and the spillover lets an attacker change what the device does next. Zyxel's advisory, published in June 2026, says the problem sits in the CGI program of the GS1900 series switch firmware, meaning the software built into the device that answers web requests. A CGI program is the small component that handles requests arriving over the web. According to the advisory, an attacker on the same local network (a LAN, the network inside an office, shop or home) needs no account and no password, a condition described as unauthenticated, and can send a specially crafted HTTP request, the same kind of message a browser sends to a website, to run operating system commands on the switch.
Zyxel has released fixed firmware for the affected models. The GS1900-8 at 2.90(AAHH.1)C0 and earlier is fixed in 2.90(AAHH.2)C0; the GS1900-8HP at 2.90(AAHI.1)C0 and earlier is fixed in 2.90(AAHI.2)C0; the GS1900-10HP at 2.90(AAZI.1)C0 and earlier is fixed in 2.90(AAZI.2)C0; the GS1900-16 at 2.90(AAHJ.1)C0 and earlier is fixed in 2.90(AAHJ.2)C0; the GS1900-24 at 2.90(AAHL.1)C0 and earlier is fixed in 2.90(AAHL.2)C0; the GS1900-24E at 2.90(AAHK.1)C0 and earlier is fixed in 2.90(AAHK.2)C0; the GS1900-24EP at 2.90(ABTO.1)C0 and earlier is fixed in 2.90(ABTO.2)C0; the GS1900-24HPv2 at 2.90(ABTP.1)C0 and earlier is fixed in 2.90(ABTP.2)C0; the GS1900-48 at 2.90(AAHN.1)C0 and earlier is fixed in 2.90(AAHN.2)C0; and the GS1900-48HPv2 at 2.90(ABTQ.1)C0 and earlier is fixed in 2.90(ABTQ.2)C0. Anyone running one of these switches should compare the firmware version shown in the device to this list.
The scale of the abuse is documented by GreyNoise, a company that studies attack traffic, which reported a suspected Chinese-speaking malicious actor that has been weaponizing the flaw since August 17, 2026. According to GreyNoise, the attacker successfully exploited and exfiltrated data from 996 Zyxel switches across 48 countries, among them Italy, the United States, Taiwan, France and South Korea. The attacker used the exploit to run the Trivial File Transfer Protocol (TFTP) tool, a simple way of moving files onto a device, in order to pull down and run a custom collector script. The data taken covers device configurations, hashed root-level credentials (passwords stored in scrambled form, which are valuable because they can sometimes be cracked back to the original) and networking information. GreyNoise added that the exploit code sat inside a Python script heavily obfuscated with PyArmor, a commercial tool that makes code hard to read. GreyNoise also noted that while the script explicitly targets firmware versions 2.10 to 2.90 of the GS1900-24, it offers command line options such as a libc base address and global offsets for targeting other firmware in scope for the vulnerability, which suggests the tooling can be pointed at further models.
The same activity has a wider reach. GreyNoise's cluster is either the same as, or overlaps with, an actor that Acronis disclosed last week, which abused a recently disclosed flaw in Gitea (CVE-2026-60004) to break into internet-facing instances. Acronis, a cybersecurity company, tracks that activity under the name Red Heron. Beyond Gitea and Zyxel, the adversary has been seen exploiting flaws in UniFi OS (CVE-2026-34908, CVE-2026-34909 and CVE-2026-34910), Flowise (CVE-2026-56271), WordPress (CVE-2026-63030 and CVE-2026-60137), the Linux kernel (CVE-2022-0847), Nuclio (CVE-2026-79756), SENAITE LIMS (CVE-2026-54569), Proxmox VE (CVE-2023-54391) and an unspecified issue in Palo Alto Networks PAN-OS GlobalProtect portals. The WordPress entries matter to a very large number of site owners, because the publishing software is so widely deployed.
On the Zyxel side, the vendor credited Lei Gu, Jun Cao, Zhiqing Rui, Jingzheng Wu and Tianyue Luo from ISCAS with discovering and reporting the vulnerability. At the time the source material was written, Zyxel had not yet revised its alert to confirm that the flaw is being exploited in the wild, which means the exploitation evidence currently comes from CISA and GreyNoise rather than from the vendor's own advisory. In light of the active exploitation, Federal Civilian Executive Branch (FCEB) agencies in the United States are required to apply the fixes by September 24, 2026. That deadline is a useful signal for everyone else about how urgently this one is being treated.
A second, separate flaw is also under active attack. Arctic Wolf warned of exploitation of CVE-2026-32996, a local privilege escalation vulnerability with a CVSS score of 7.3 in Veeam Agent for Microsoft Windows. A local privilege escalation means someone who already has some kind of access to the machine can climb to a higher level of control than they were given. In this case, the attacker ends up with SYSTEM-level control of the affected endpoint, SYSTEM being the highest privilege level on Windows. Arctic Wolf explains that the problem lies in how the Veeam Endpoint Backup service handles elevated client sessions over a local gRPC named pipe, written as \\.\pipe\Veeam\VAW\ServiceConnectionPipe. In plain terms, a named pipe is a channel programs on the same computer use to talk to each other. Arctic Wolf states that the service caches an elevated administrator identity against a session identifier that the client controls, and that this identifier is not bound to the user or the connection that requested it. Because those elevated session identifiers are written into the file C:\ProgramData\Veeam\Endpoint\Svc.VeeamEndpointBackup.log, which ordinary users can read, an attacker can obtain a valid identifier and use it to run commands as SYSTEM. According to Arctic Wolf, a public proof of concept on GitHub demonstrates the weakness by running whoami, a Windows command that reports which account is in use, and writing the result to a file.
For businesses, the pattern across both stories is the same as it always is with exploited flaws: the fixes exist and the delay in applying them is what attackers count on. Network switches sit quietly in cupboards and rarely get updated, yet a compromised one can hand over configuration data and credential material for the rest
How to Protect Yourself
- If your office uses a Zyxel GS1900 switch, ask whoever looks after your network to install the fixed firmware version for your exact model and then restart the device.
- On any Windows computer that has Veeam Agent installed, install the latest Veeam update, because the flaw only matters until it is patched.
- Let only people you genuinely trust use your work computers and never share one administrator login between several people, since this second flaw needs someone to already be logged in to the machine.
- Turn on automatic updates for Windows and for the backup and security programs you use, so fixes arrive without you having to remember them.
- Ask your IT contact to check the software your business runs behind the scenes, such as switch firmware and backup tools, and to tell you what has been updated and what has not.
- If you run a WordPress site, keep the site and its plugins updated as well, because the same attackers were seen going after WordPress flaws.
Vulnerabilities & Fixes
- CVE-2022-0847 A Linux kernel vulnerability listed among the flaws exploited by the same cluster. View the fix & details →
- CVE-2023-54391 A Proxmox VE vulnerability listed among the flaws exploited by the same cluster. View the fix & details →
- CVE-2026-32996 Local privilege escalation in Veeam Agent for Microsoft Windows that lets an attacker with local access gain SYSTEM-level control through the Endpoint Backup service. View the fix & details →
- CVE-2026-34908 One of three UniFi OS flaws the adversary has been observed exploiting. View the fix & details →
- CVE-2026-34909 One of three UniFi OS flaws the adversary has been observed exploiting. View the fix & details →
- CVE-2026-34910 One of three UniFi OS flaws the adversary has been observed exploiting. View the fix & details →
- CVE-2026-54569 A SENAITE LIMS vulnerability listed among the flaws exploited by the same cluster. View the fix & details →
- CVE-2026-56271 A Flowise vulnerability listed among the flaws exploited by the same activity. View the fix & details →
- CVE-2026-60004 A recently disclosed Gitea vulnerability abused by the cluster Acronis tracks as Red Heron to break into internet-facing instances. View the fix & details →
- CVE-2026-60137 A WordPress vulnerability the adversary has been observed exploiting. View the fix & details →
- CVE-2026-63030 A WordPress vulnerability the adversary has been observed exploiting. View the fix & details →
- CVE-2026-7273 Stack-based buffer overflow in the CGI program of Zyxel GS1900 series switch firmware, allowing an unauthenticated attacker on the local network to run operating system commands; fixed in the newer 2.90 firmware releases listed by Zyxel. View the fix & details →
- CVE-2026-79756 A Nuclio vulnerability listed among the flaws exploited by the same cluster. View the fix & details →
Terms Explained
- CVE A standard reference number given to a publicly known security flaw so that everyone can identify the same bug.
- CVSS score A number from 1 to 10 that shows how serious a security flaw is, where a higher number means more risk.
- stack-based buffer overflow A type of bug where a program is made to stuff more information into a small memory space than it can hold, which lets an attacker influence what the program does next.
- firmware The permanent software built into a device such as a switch or router, which you update to fix problems.
- LAN The local network inside one building or home, where the devices can reach each other without going out to the internet.
- privilege escalation When someone who already has limited access to a computer finds a way to gain much greater control over it.
- SYSTEM The highest level of permission on a Windows computer, able to do anything on the machine.
- proof of concept A small demonstration, often shared publicly, showing that a security flaw can really be used.